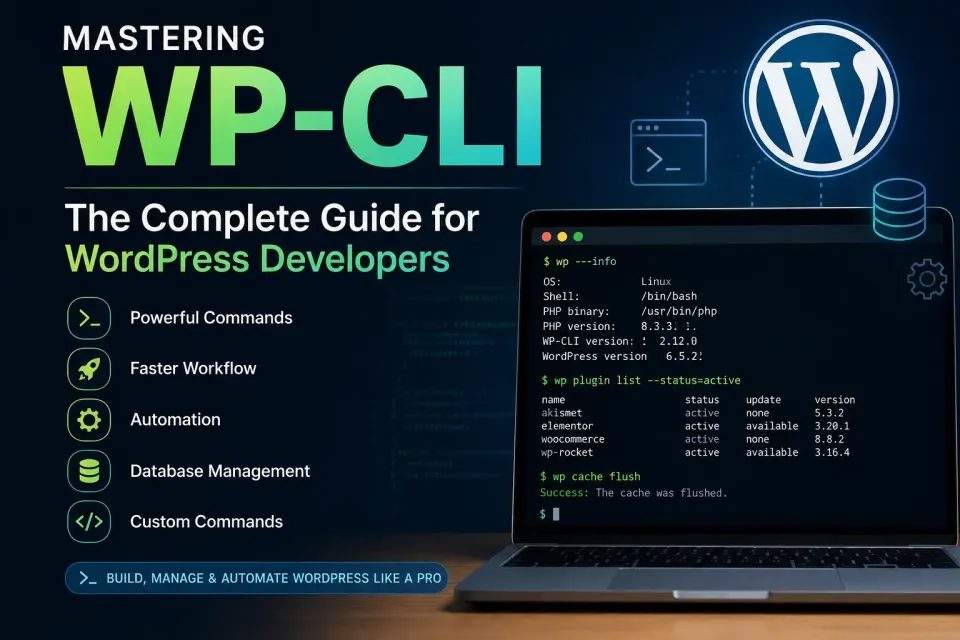
Mastering WP-CLI: A Complete Guide for Intermediate WordPress Developers
Install plugins, update themes, manage users and run database tasks from the terminal in seconds, instead of clicking through the admin.
WordPress itself is secure. Most problems come from avoidable mistakes: here are the common ones, and how to avoid them.
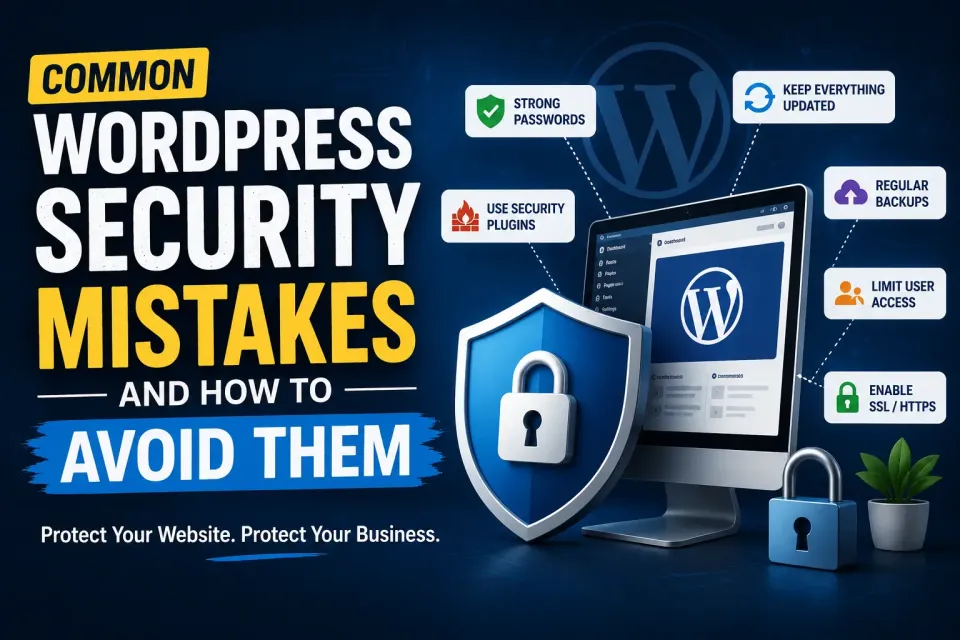
If you’re running a WordPress website, security should never be an afterthought. Whether you own a business website, an online store, or a personal blog, your site is constantly exposed to automated attacks, malware, and hackers looking for vulnerabilities.
The good news is that WordPress itself is a secure platform. The majority of security issues occur because of poor maintenance, weak passwords, outdated plugins, or simple configuration mistakes. Most of these problems are completely avoidable with a few best practices.
In this guide, we’ll explore the most common WordPress security mistakes and show you practical ways to protect your website from cyber threats.
WordPress powers more than 40% of all websites on the internet, making it the world’s most popular content management system. Its popularity also makes it a frequent target for attackers.
A compromised website can lead to:
Fortunately, securing a WordPress website doesn’t require advanced technical skills. By avoiding a few common mistakes, you can significantly reduce your risk.
One of the biggest mistakes website owners make is delaying updates for WordPress core, themes, and plugins.
Developers regularly release updates to fix bugs, improve performance, and patch security vulnerabilities. Running outdated software leaves known security holes that attackers can easily exploit.
How to avoid it
Weak passwords remain one of the easiest ways for hackers to gain access to a website through brute-force attacks.
Passwords like:
can often be cracked within minutes.
How to avoid it
Use strong passwords that include:
A secure password manager can generate and store complex passwords, so you don’t have to remember them.
Also encourage every user with website access to use strong, unique passwords.
Many WordPress websites still use “admin” as the administrator username.
If hackers already know your username, they only need to guess your password.
How to avoid it
Create a new administrator account with a unique username and delete the old “admin” account.
Examples:
Avoid obvious usernames that are easy to guess.
Free versions of premium plugins from unofficial websites may seem tempting, but they often contain hidden malware, spam links, or backdoors.
These malicious files can silently:
How to avoid it
Always download plugins and themes from trusted sources such as:
If a premium plugin seems “too good to be free,” it’s usually not worth the risk.
More plugins don’t necessarily mean better functionality.
Every additional plugin increases your website’s attack surface. Poorly coded or abandoned plugins can introduce serious vulnerabilities.
How to avoid it
Instead of counting plugins, focus on quality.
Before installing a plugin, check:
Remove plugins you no longer use.
A lean website is generally safer and easier to maintain.
Your hosting provider plays a critical role in website security.
Low-quality hosting often lacks:
If one website on a poorly managed shared server gets infected, others may also be affected.
How to avoid it
Choose a reliable hosting provider that offers:
Although quality hosting may cost a little more, it’s far less expensive than recovering from a hacked website.
An SSL certificate encrypts the data exchanged between your website and visitors. Without HTTPS, sensitive information such as login credentials or contact form submissions can be intercepted.
In addition, modern browsers display “Not Secure” warnings for websites without SSL, which can reduce visitor trust and even affect conversions.
How to avoid it
Most reputable hosting providers now include free SSL certificates, so there’s little reason to leave your website unsecured.
Many website owners assume their hosting provider handles all security. While good hosting adds an important layer of protection, it’s not enough on its own.
A reliable WordPress security plugin can help detect malware, block suspicious login attempts, scan files for changes, and notify you of potential threats.
How to avoid it
Install a trusted security plugin and configure its essential features, such as:
Remember, a security plugin is only effective if you keep it updated.
Imagine waking up one morning to find your website hacked or accidentally deleted. Without a recent backup, restoring your website can be difficult—or even impossible.
Backups are your safety net.
How to avoid it
Follow the 3-2-1 backup rule:
Schedule automatic backups daily for busy websites or weekly for smaller sites. Test your backups occasionally to ensure they can actually be restored.
Not every team member needs full control over your website.
Granting administrator access to writers, editors, or freelancers increases the risk of accidental changes or compromised accounts.
How to avoid it
Use WordPress roles wisely:
Follow the principle of least privilege by giving users only the permissions they need.
Passwords alone are no longer enough to protect your website.
Even a strong password can be exposed through phishing, malware, or data breaches.
How to avoid it
Enable Two-Factor Authentication (2FA) for administrator accounts.
With 2FA enabled, users must verify their identity using an authentication app or one-time code in addition to their password.
This extra step significantly reduces the risk of unauthorized access.
The default WordPress login page (/wp-login.php) is one of the most common targets for brute-force attacks.
Hackers use automated bots to repeatedly guess usernames and passwords.
How to avoid it
Protect your login page by:
These measures make it much harder for automated bots to attack your website.
In addition to avoiding the mistakes above, adopt these habits:
Security isn’t a one-time task. It’s an ongoing process that requires regular attention.
Use this quick checklist to strengthen your website’s security:
If you can check every item on this list, your website will be far better protected than many WordPress sites online.
More guides from the Magexweb blog.
Install plugins, update themes, manage users and run database tasks from the terminal in seconds, instead of clicking through the admin.
Shipping costs are a common reason shoppers abandon a cart. Here’s how a free shipping bar nudges them to add one more item instead.
Why patching on time matters, and how to install Magento 2 security patches with Composer or by hand.
Upgrades, security patches and platform moves are what we do every day. Tell us what your site needs, and we will reply with questions and next steps.
0 Comments
No comments yet. Be the first to comment.
Leave a Comment
Please sign in to comment. Sign in